加密与解密:同一封信的两种样子Encryption and Decryption: Two Forms of a Message
字母转盘说明了密钥。现在小禾想知道:收信人怎样把看不懂的内容还原回来?The alphabet wheel introduced keys. How can a recipient recover the original message?
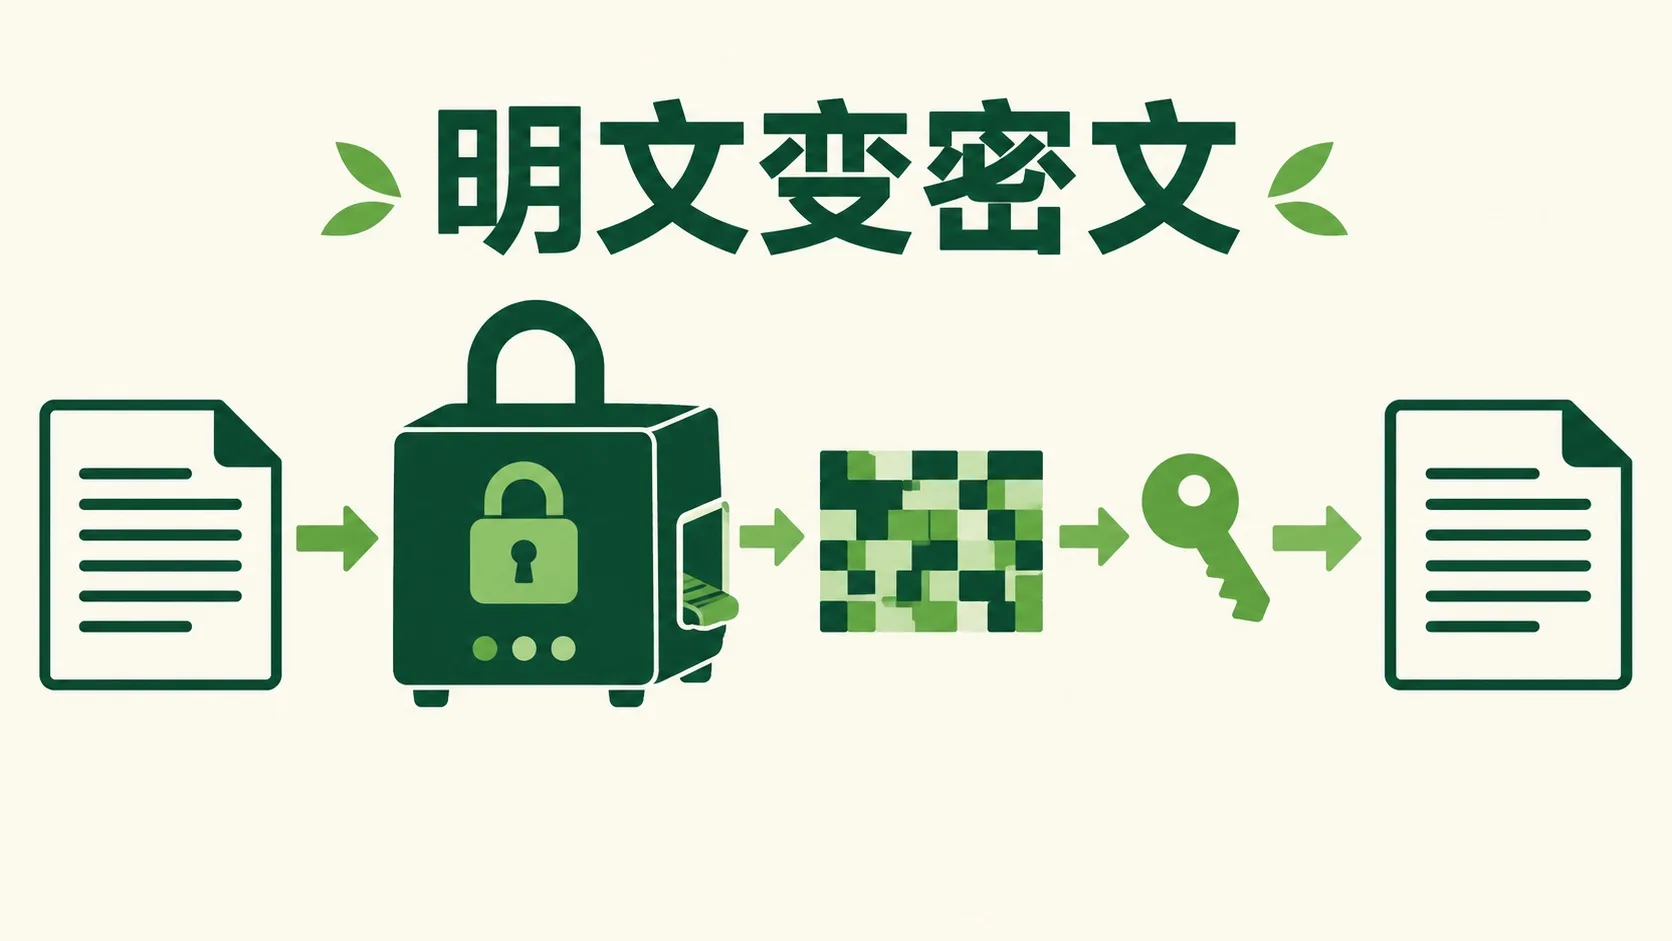
第 1 步:从明文到密文Step 1: From plaintext to ciphertext
把信息变乱,还要能按规则还原。The transformation must have a defined reversal.
明文是原始信息,密文是加密后的表示。解密用合适密钥恢复明文。编码和压缩也会改变外观,却不等于加密。比如把文字转成二进制,不会自动保密。小禾关心的是:没有密钥的人,是否难以获取内容。Plaintext is the original information; ciphertext is its encrypted representation. Decryption recovers plaintext using the appropriate key. Encoding and compression also alter appearance but are not encryption. Converting text to binary does not automatically make it secret. The question is whether recovery is difficult without the key.
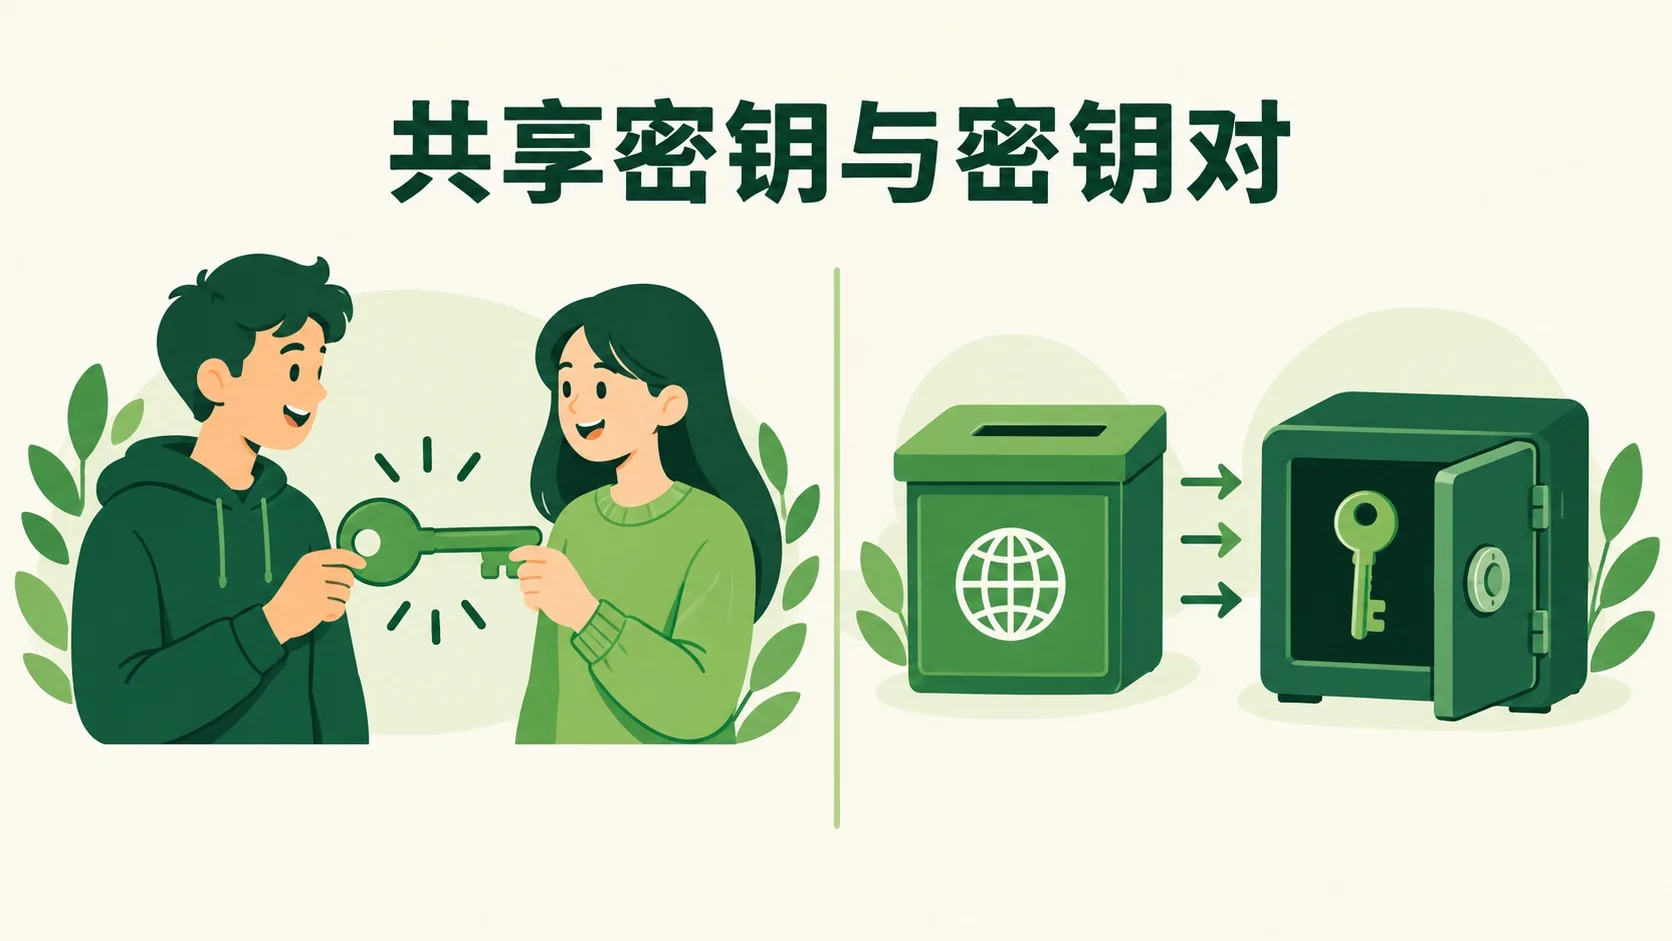
第 2 步:共享秘密,或使用一对钥匙Step 2: Shared secrets or paired keys
所有人都用同一把钥匙吗?Does every scheme use the same key at both ends?
对称加密用共享秘密完成加解密。双方先要安全地建立或取得密钥。非对称机制使用公钥与私钥。公钥可以分发,私钥需要保密。不同公钥算法支持的用途不同。实际通信常结合密钥协商与对称加密,不能把所有机制都想成两把实体锁匙。Symmetric encryption uses a shared secret for encryption and decryption, so the parties need a secure way to establish it. Asymmetric mechanisms use public and private keys. The public key can be distributed; the private one stays secret. Algorithms support different operations. Real protocols often combine key agreement and symmetric encryption.
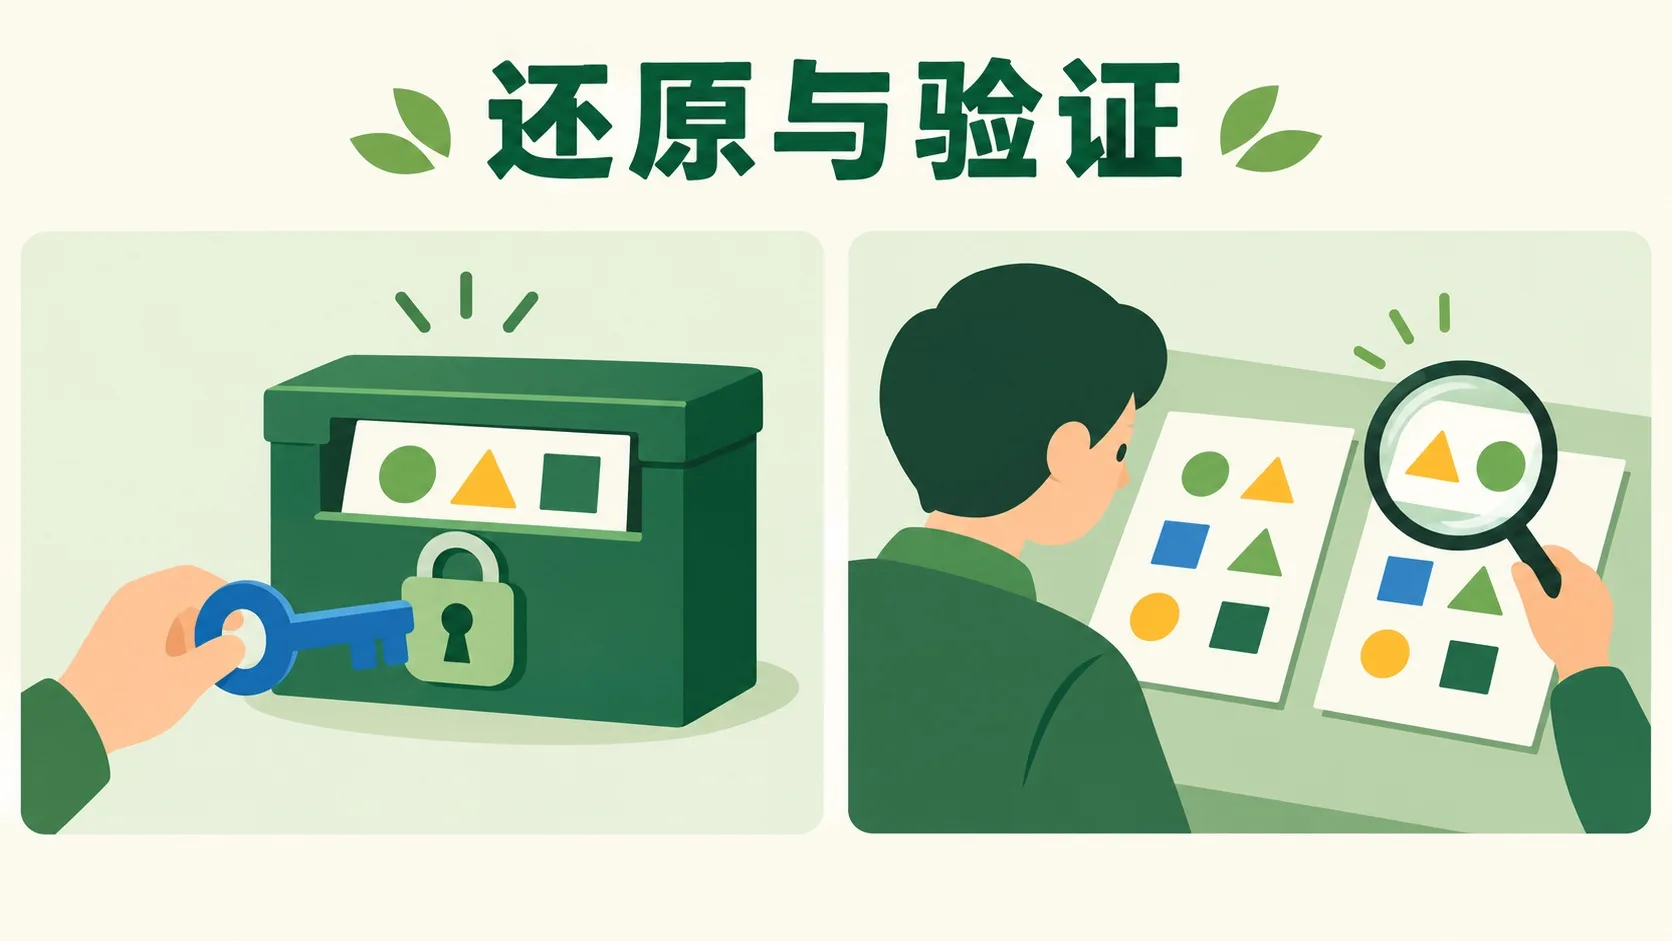
第 3 步:还原出来,也要验证Step 3: Recovery also needs validation
解密有输出,就一定没有被改吗?Does decryption output prove nothing was altered?
有的方案解密后会给出一串数据,却不能保证内容未改。认证加密把保密与篡改检测结合起来。下面用异或做四位二进制练习。相同位得零,不同位得一;再用同一串位异或,可恢复原文。这个小例子不等于安全的真实加密协议。Some schemes output data on decryption without assuring it was not changed. Authenticated encryption combines secrecy with tamper detection. Below, four-bit XOR yields zero for equal bits and one for unequal bits. Applying the same key bits again restores the original. This small exercise is not a secure real-world protocol.
🎮 四位密钥工作台🎮 Four-bit key workbench
点亮四个密钥位,把密文还原成每轮指定明文。观察每一位的异或结果。Toggle four key bits to recover the requested plaintext. Observe XOR for every bit.
一句话记住它:Remember: 加密把明文变成密文,解密还原;真实系统还要验证完整性。Encryption transforms plaintext; decryption recovers it. Real systems also need integrity checks.
编码不等于加密。Encoding is not encryption.密钥建立与保存是关键环节。Key establishment and storage matter.练习里的短密钥没有真实安全性。The short teaching key has no practical security.
 Back to tree