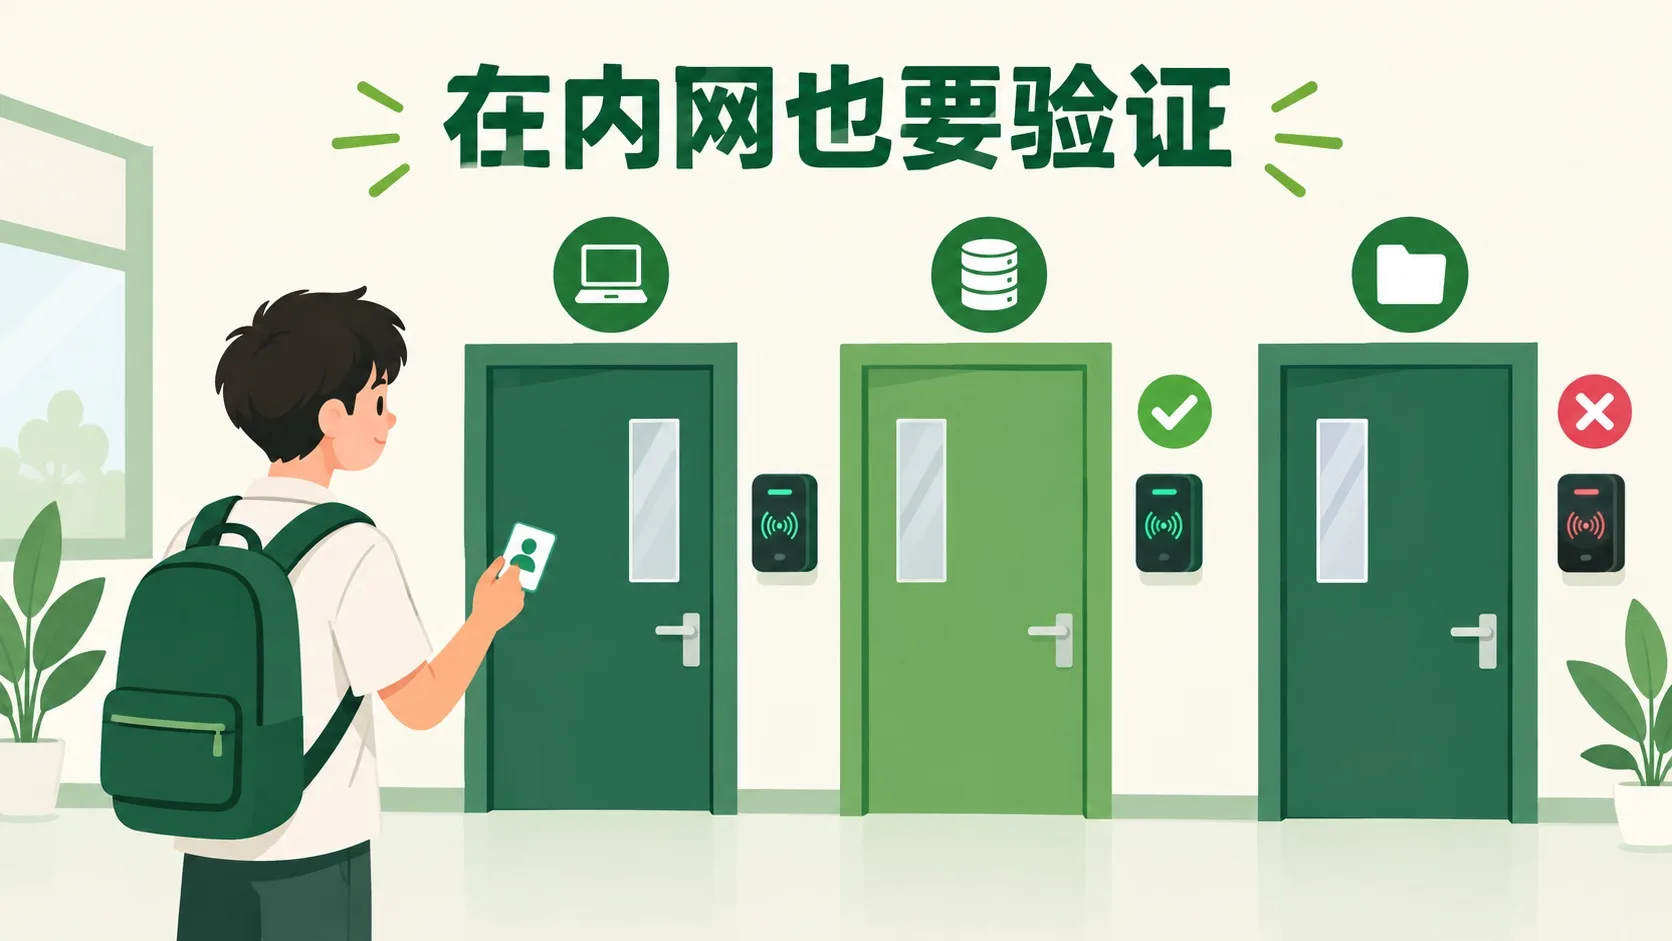
同学连上学校网络,就能打开全部班级资料吗?小禾发现:在门里,不代表每个房间都该进去。Does joining the school network grant access to every class file? Being inside a building should not open every room.
第 1 步:位置不能自动换来信任Step 1: Location is not automatic trust
已经进了内网,为什么还检查?Why check a request already inside the network?
零信任不因为网络位置就默认放行。它关注具体用户、设备和资源。账号可能被盗,设备也可能失去安全状态。授权应根据明确的身份与策略决定。这个名字不是要求怀疑所有人品,而是不要把“在里面”当作充分证据。Zero trust does not grant access solely because of network location. It considers users, devices and resources. Accounts can be stolen and device posture can change. Authorization needs explicit identity and policy evidence. The name is not a judgment about people’s character: being inside is insufficient evidence by itself.
第 2 步:权限够用就好Step 2: Grant only needed access
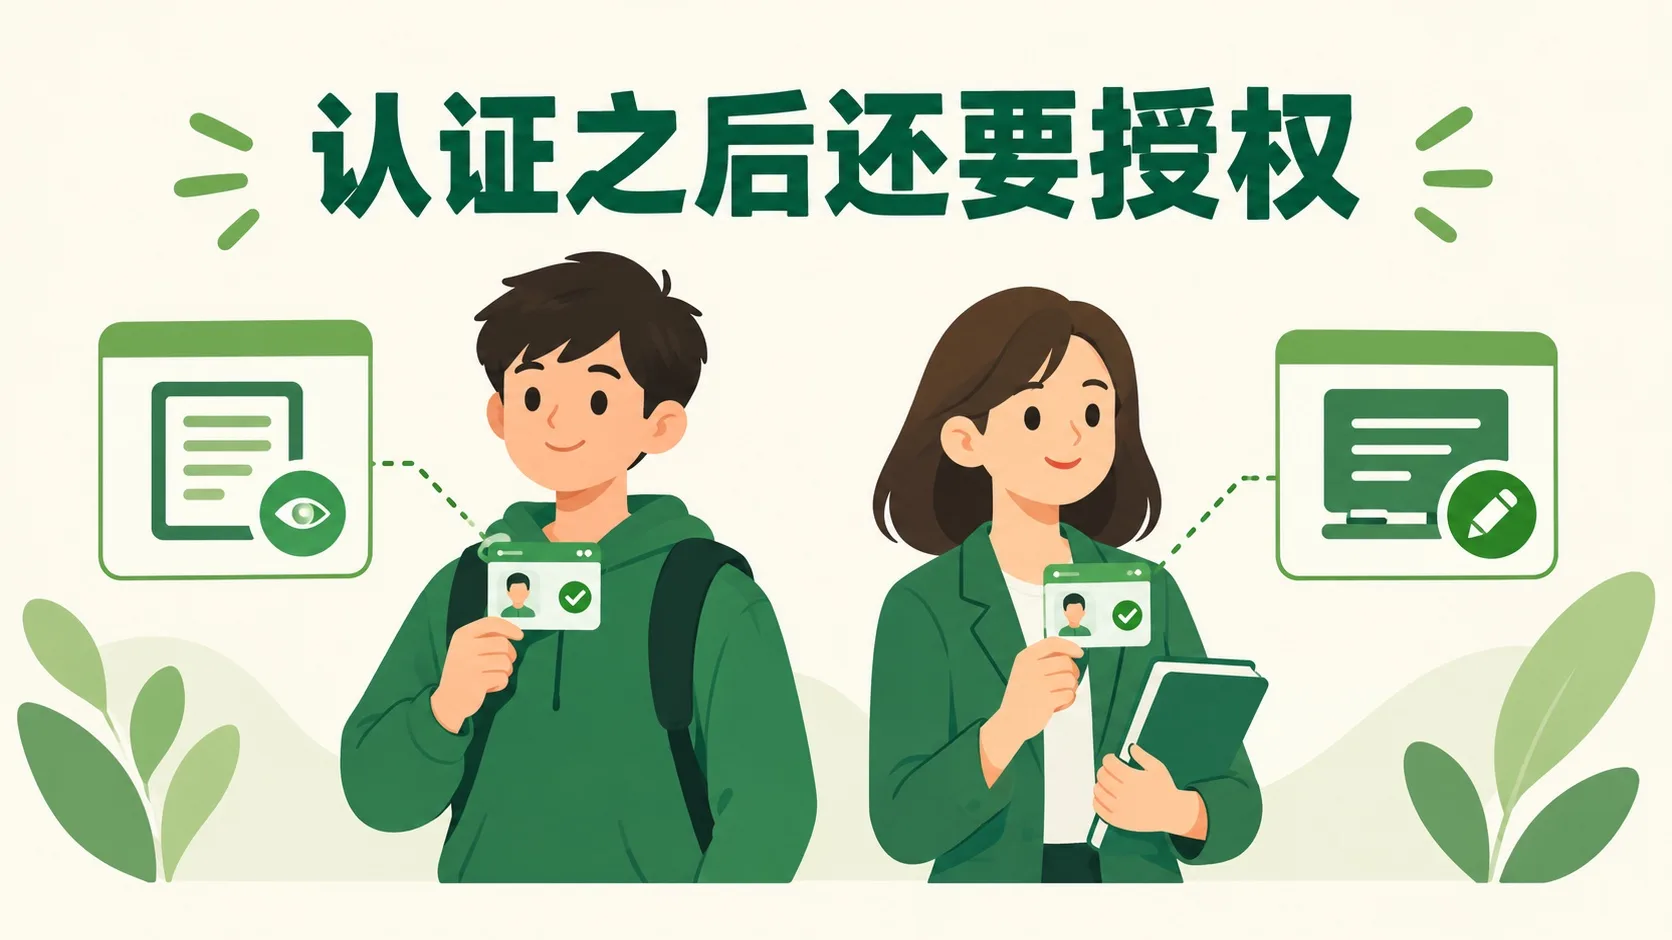
验证了身份,就能拿全部权限吗?Does authentication justify every permission?
认证回答你是谁,授权回答你能做什么。阅览通知和修改成绩需要不同权限。最小权限是只授予任务所需的能力。小禾给同学阅览权,给老师特定修改权。设备状态、风险和会话条件也可参与决定。不该为了方便永久开放所有资源。Authentication asks who you are; authorization asks what you may do. Reading a notice and editing grades require different permissions. Least privilege grants only what a task needs. Classmates get reading access and teachers narrowly scoped editing access. Device posture, risk and session conditions can also affect decisions.
第 3 步:情况变化就重新评估Step 3: Reassess when conditions change
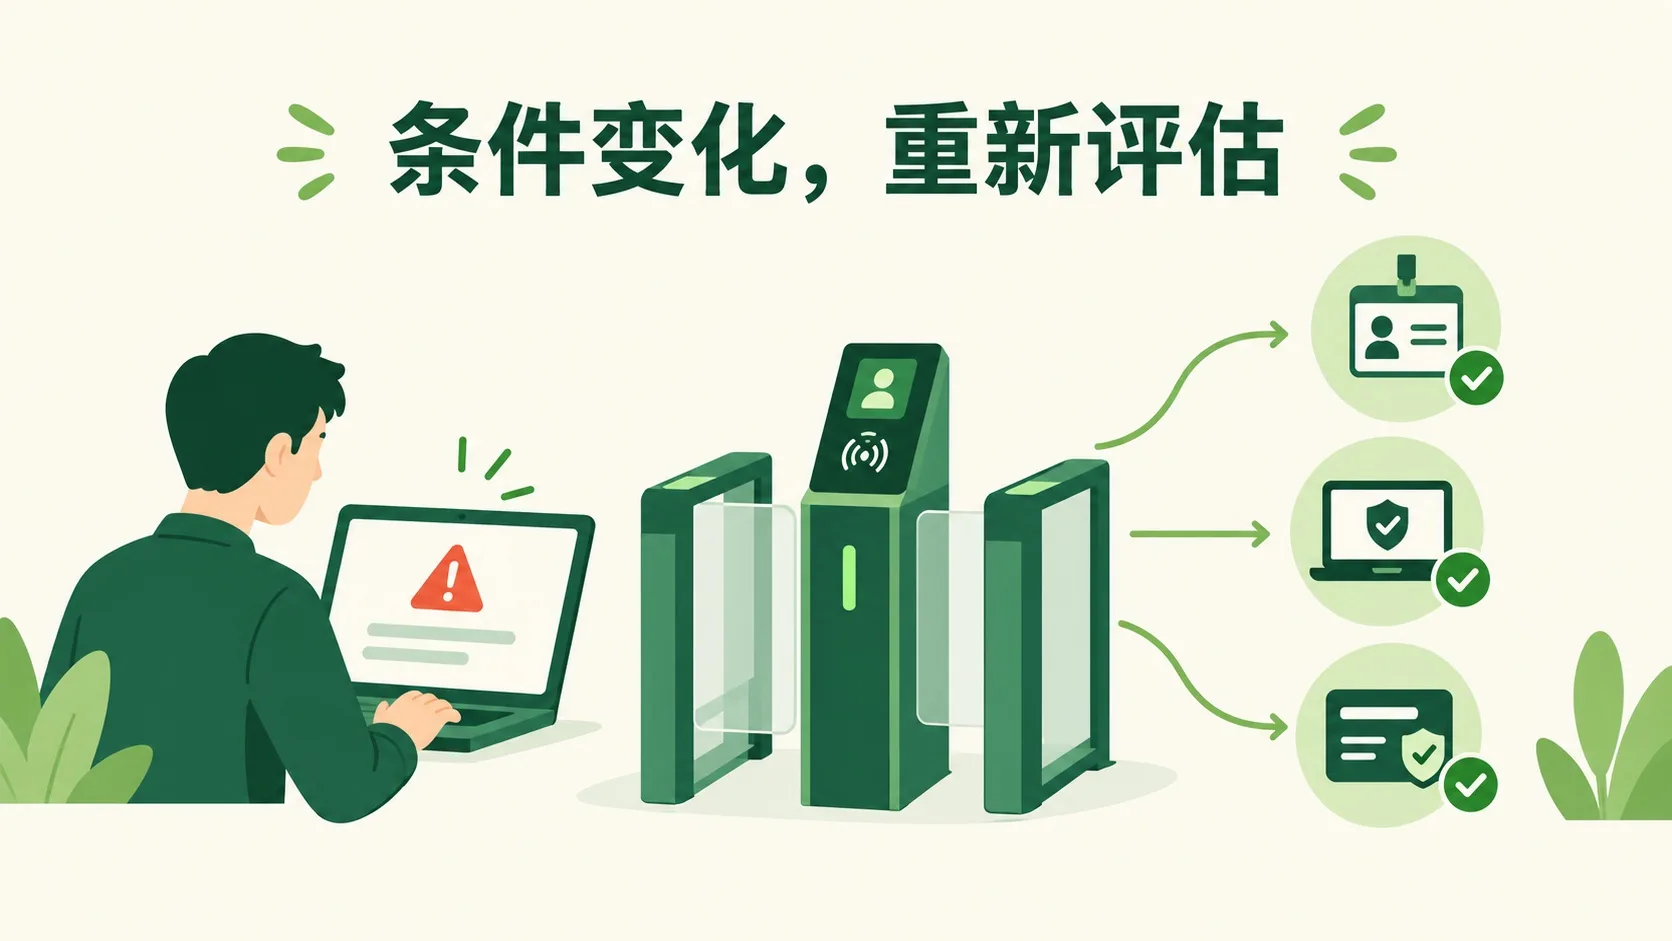
刚才允许的访问,之后还一定允许吗?Does a previous allow decision last forever?
设备变得不合规或凭证失效时,系统可能需要重新判断。记录和监测帮助发现变化。零信任是一组架构原则,不是一件买来就完成的产品。部署要适合实际任务,兼顾可用性与隐私。练习把三项条件简化成开关,真实策略通常复杂得多。A device becoming noncompliant or credentials expiring may require reassessment. Logs and monitoring help detect changes. Zero trust is a set of architectural principles, not a product that completes the job when purchased. Deployment must fit the task and consider usability and privacy. Three switches simplify much richer real policies.
🎮 资料室访问实验🎮 Resource access experiment
根据四个访问场景,设置身份、设备与权限条件,观察为什么放行或拒绝。Set identity, device and permission conditions for four requests and inspect why access is allowed or denied.
一句话记住它:Remember: 不按位置默认信任,按身份、资源与策略授予必要访问。Grant necessary access based on identity, resource and policy rather than location alone.
认证与授权不是同一步。Authentication and authorization are different.权限应匹配当前任务。Permissions should fit the current task.条件变化需要重新评估。Changed conditions require reassessment.
把握度:NIST 架构原则较高。三开关是教学简化,不代表完整安全产品。Confidence: high for the NIST architectural principles. Three switches are a teaching simplification, not a complete security product.
AI 辅助制作与资料核对。插图和互动为教学示意。AI-assisted production and source checking. Illustrations and interactions are teaching models.
 Back to tree